UK operation wards off risk of cyber-attack on supermarket fridges and freezers
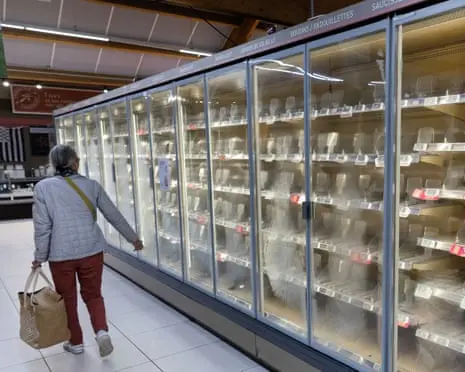
News of vulnerability comes after retailers in at least seven European countries hit by cyber-attacks A secret government cybersecurity operation recently warded off the risk of a cyber-attack on fridges and freezers in UK supermarkets, warehouses, restaurants, petrol stations and stadiums, it has emerged. An attack would have been similar to those that have caused many millions of euros of...
A secret government cybersecurity operation recently warded off the risk of a cyber-attack on fridges and freezers in UK supermarkets, warehouses, restaurants, petrol stations and stadiums, it has emerged.
An attack would have been similar to those that have caused many millions of euros of damage in continental Europe in recent months. But, while many retailers have now been protected, researchers warned that many more could still be vulnerable.
News of the operation led by Whitehall and the National Cyber Security Centre, first reported by the BBC, comes after supermarket chains in at least seven European countries were affected by a cyber-attack this month.
Another wave of attacks also affected hundreds of retailers across France in October in an act of “unprecedented scale and unprecedented aggression” for which Paris has publicly blamed Iran. The Pentagon is also investigating a suspected hack after a series of fridge malfunctions hit at least six US military bases in August.
Experts told the Guardian that, if the vulnerability in UK-based devices had been discovered and exploited before a fix was found, the consequences would have been serious.
“This incident should serve as a wake-up call for the entire refrigeration industry,” said Garry Turner-Smith of Omega Solutions, a refrigeration consultancy firm whose employee, Neil McCourt, found the vulnerability in devices manufactured by Resource Data Management (RDM).
“Had these weaknesses been discovered and exploited by someone with malicious intentions, they could potentially have gained full control of vulnerable RDM data managers and used that access to interfere with refrigeration systems across multiple sites. This raises the prospect of attacks similar to those seen in Europe,” he said.
After Omega was alerted to the weakness, the firm called in the cyber-security consultants Pen Test Partners to investigate. Both firms then raised their concerns with the manufacturer, RDM.
“We determined that there was an urgent requirement to alert supermarkets and the food supply chain to the issue and fix,” said Pen Test Partners’ managing partner, Ken Munro. “However, we also had to work quietly to avoid alerting less ethical hackers and nation states of the likes of Iran, who are active in this space.”
Munro was fortunately attending a retail industry cyber event the day the vulnerabilities were found, enabling him to meet National Cyber Security Centre representatives in person to share the intelligence.
That triggered a series of briefing calls between retailers and officials from the National Cyber Security Centre, the Department for Environment, Food and Rural Affairs and the Food Standards Agency, among others, Munro said.
He added that Pen Test Partners also tried to alert the owners of exposed devices. “Some controllers were easy to identify and thus contact the owners, but many thousands at small stores are still exposed,” he said.
“The vulnerability is not easy to find for a number of reasons, but once the method is known, it’s easy to recreate. We have not published that method, so there is still time for small operators to take their controllers off the public internet and/or apply the updated firmware.”
A National Cyber Security Centre spokesperson said it “shared important insight and security advice to ensure that organisations understood potential risks to their networks, and were taking the appropriate measures to mitigate them”.
RDM did not respond to a request for comment. Its chief executive, Ged Evans, told the BBC the vulnerability was “identified in a test environment” that “went beyond” what such exercises usually involved, as it “included dismantling our hardware”.
“In any event we have acted at pace to address this issue and have already deployed first patch releases and have been in proactive contact with our customers to flag any issues and recommend mitigatory steps,” he said.